Knowledge graph and analytics
How the knowledge graph links hosts, services, vulnerabilities and access, its two backends, and the attack-chain dashboard built from it.
The PostgreSQL record answers what a command printed. The knowledge graphknowledge graphThe graph of hosts, services, vulnerabilities and the access between them that PentAGI builds during a test when this optional feature is enabled. It shows how findings connect. answers how two findingsfindingSomething the test discovered and recorded, such as a host, a running service or a vulnerability. connect — which host runs which service, which vulnerability led to which access.
Two backends
| graphstore | graphiti | |
|---|---|---|
| Runs as | in the backend, graph in Neo4j | separate service on Neo4j |
| Enabled by | GRAPHSTORE_ | GRAPHITI_ + GRAPHITI_ |
| AgentagentAn AI agent of PentAGI: a model with its own prompt, settings and tools that does one kind of work in a flow, such as testing, writing code or searching the web. tooltoolWhat an agent acts through: a built-in capability such as the terminal, the isolated browser or web search, or a program in the sandbox such as nmap, metasploit or sqlmap. | graphstore_ | graphiti_ |
| Status | successor to graphiti | legacy, kept for comparison |
Both are scoped to one flowflowOne run of PentAGI: a goal, the tasks created from your messages, and everything the agents did along the way.: every read filters by it, so one flow never sees another flow's graph.
Both backends are off by default. With GRAPHSTORE_, the graphstore needs GRAPHSTORE_ and GRAPHSTORE_, and PentAGI does not start without them.
With Graphiti enabled too, the two backends store assets differently, so PentAGI refuses to start when both write a database of the same name on one server, or on any server while Graphiti's NEO4J_ is unset, unless GRAPHSTORE_. The bundled Neo4j is Community and serves only the neo4j database: with both backends on it, keep neo4j and allow sharing, at a cost in graph quality, since ports and services are stored twice and some Graphiti writes can be rejected. To keep the graphs apart, give the graphstore its own Neo4j server, or its own database on Neo4j Enterprise: PentAGI creates that database when missing if the graphstore's Neo4j account may create databases; otherwise create it beforehand.
Attack-chain dashboard
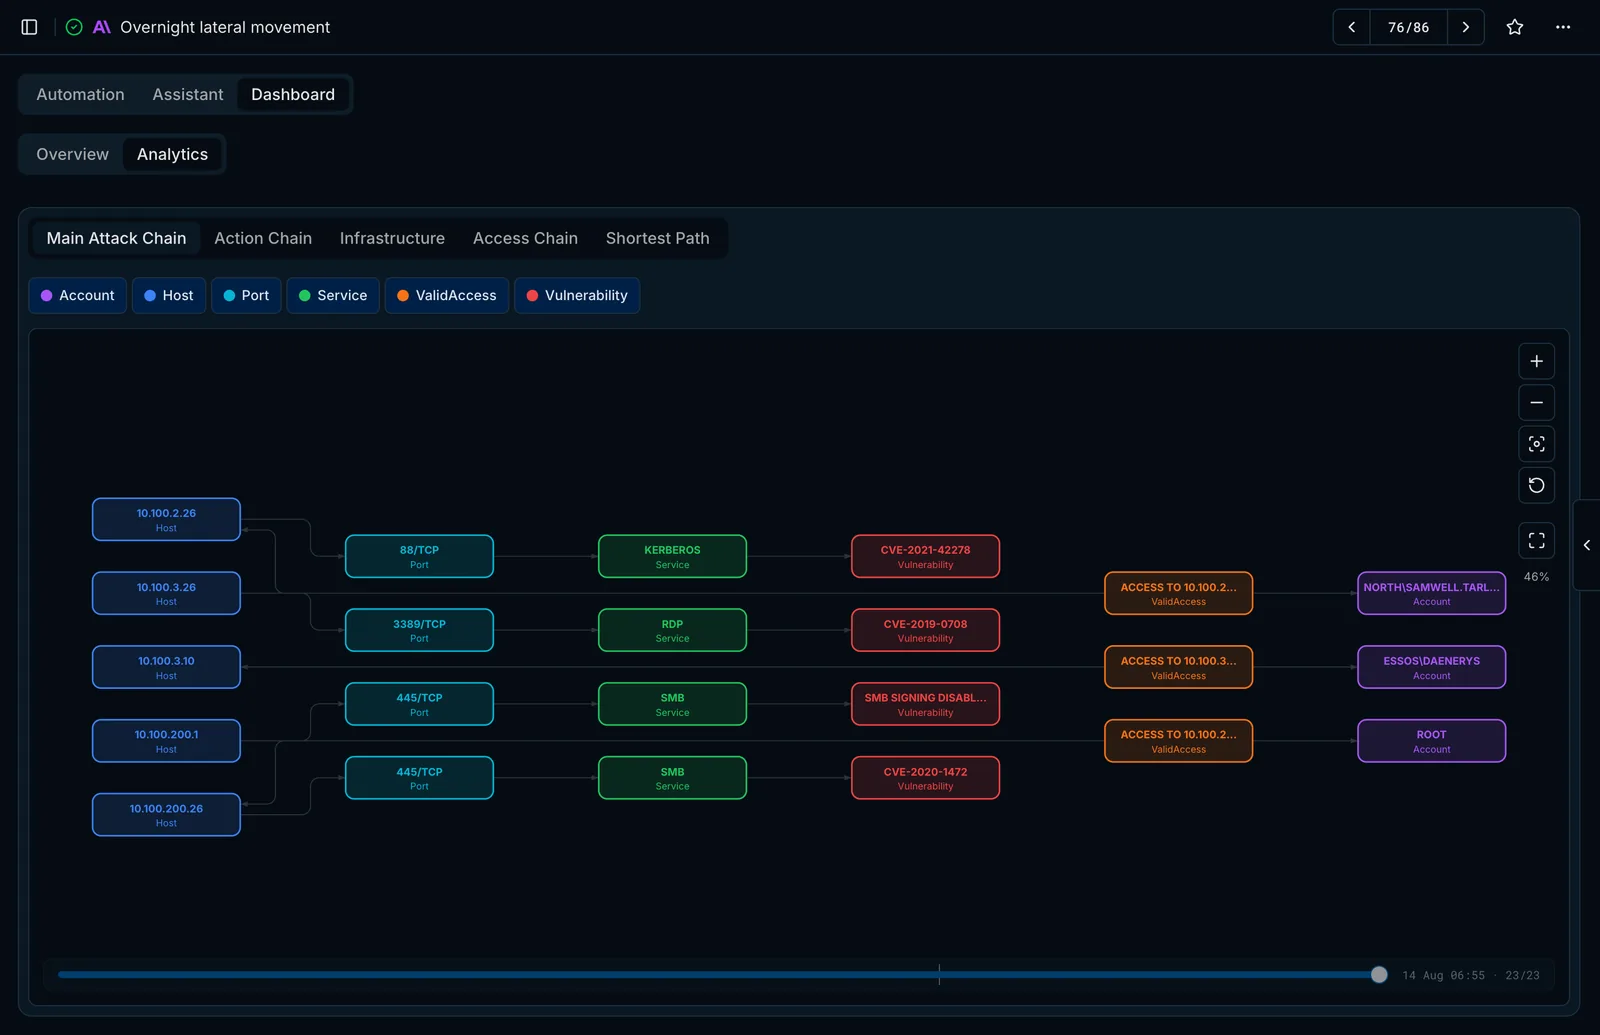
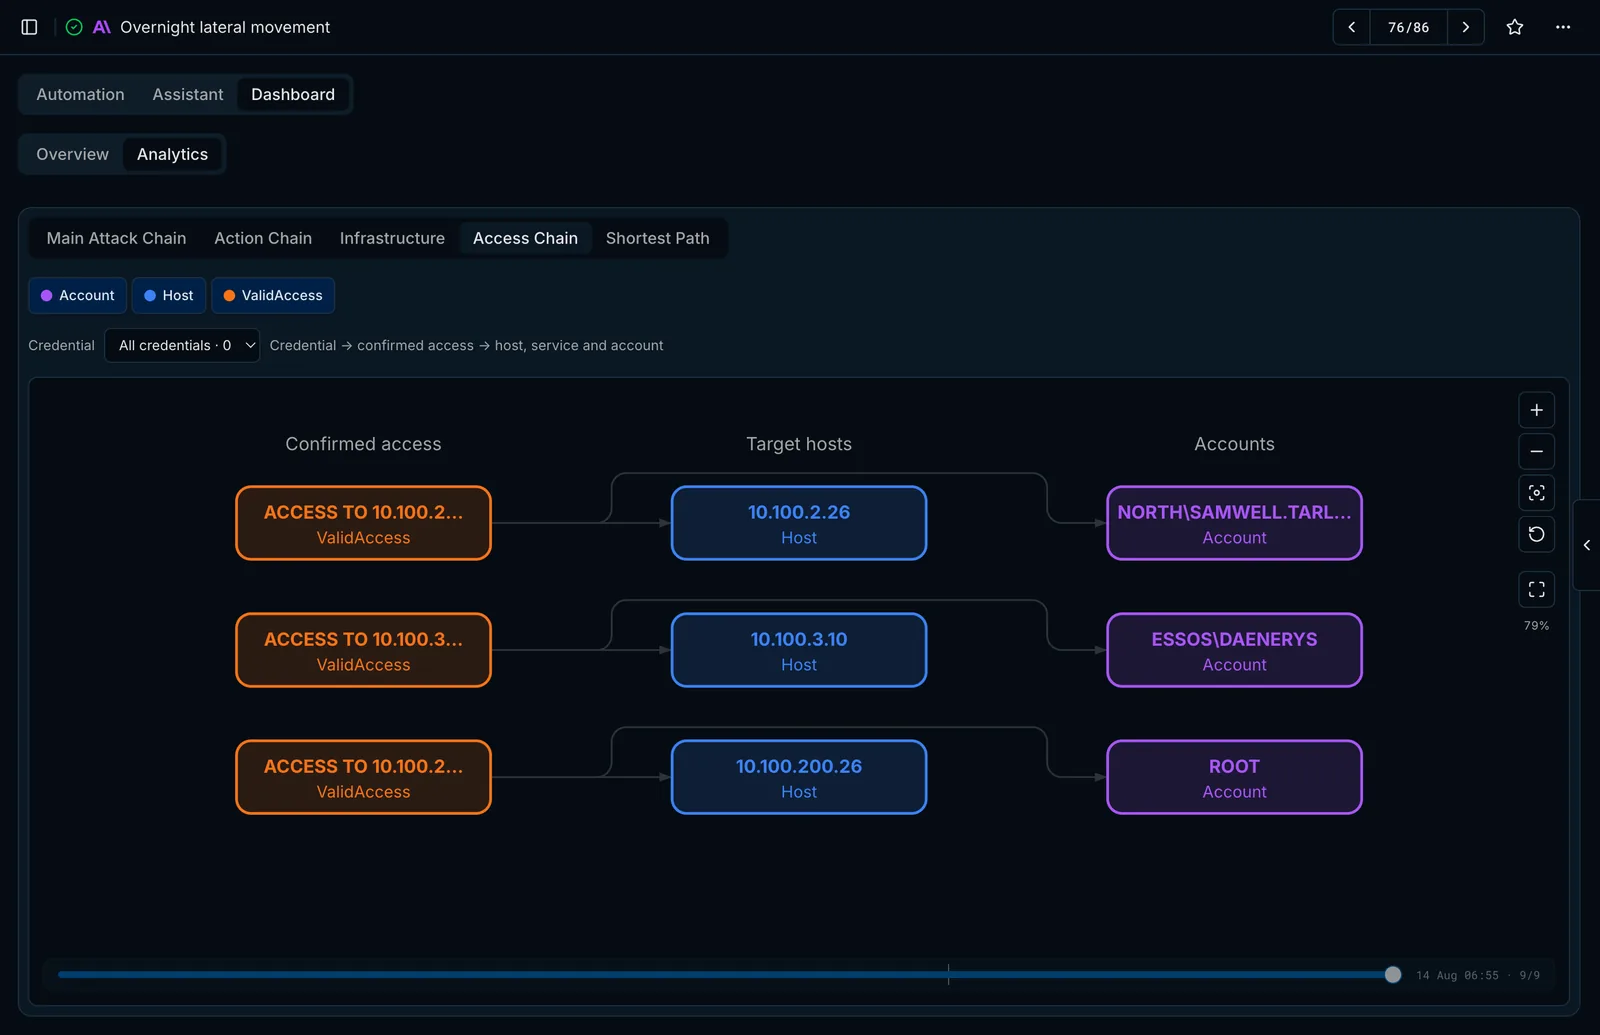
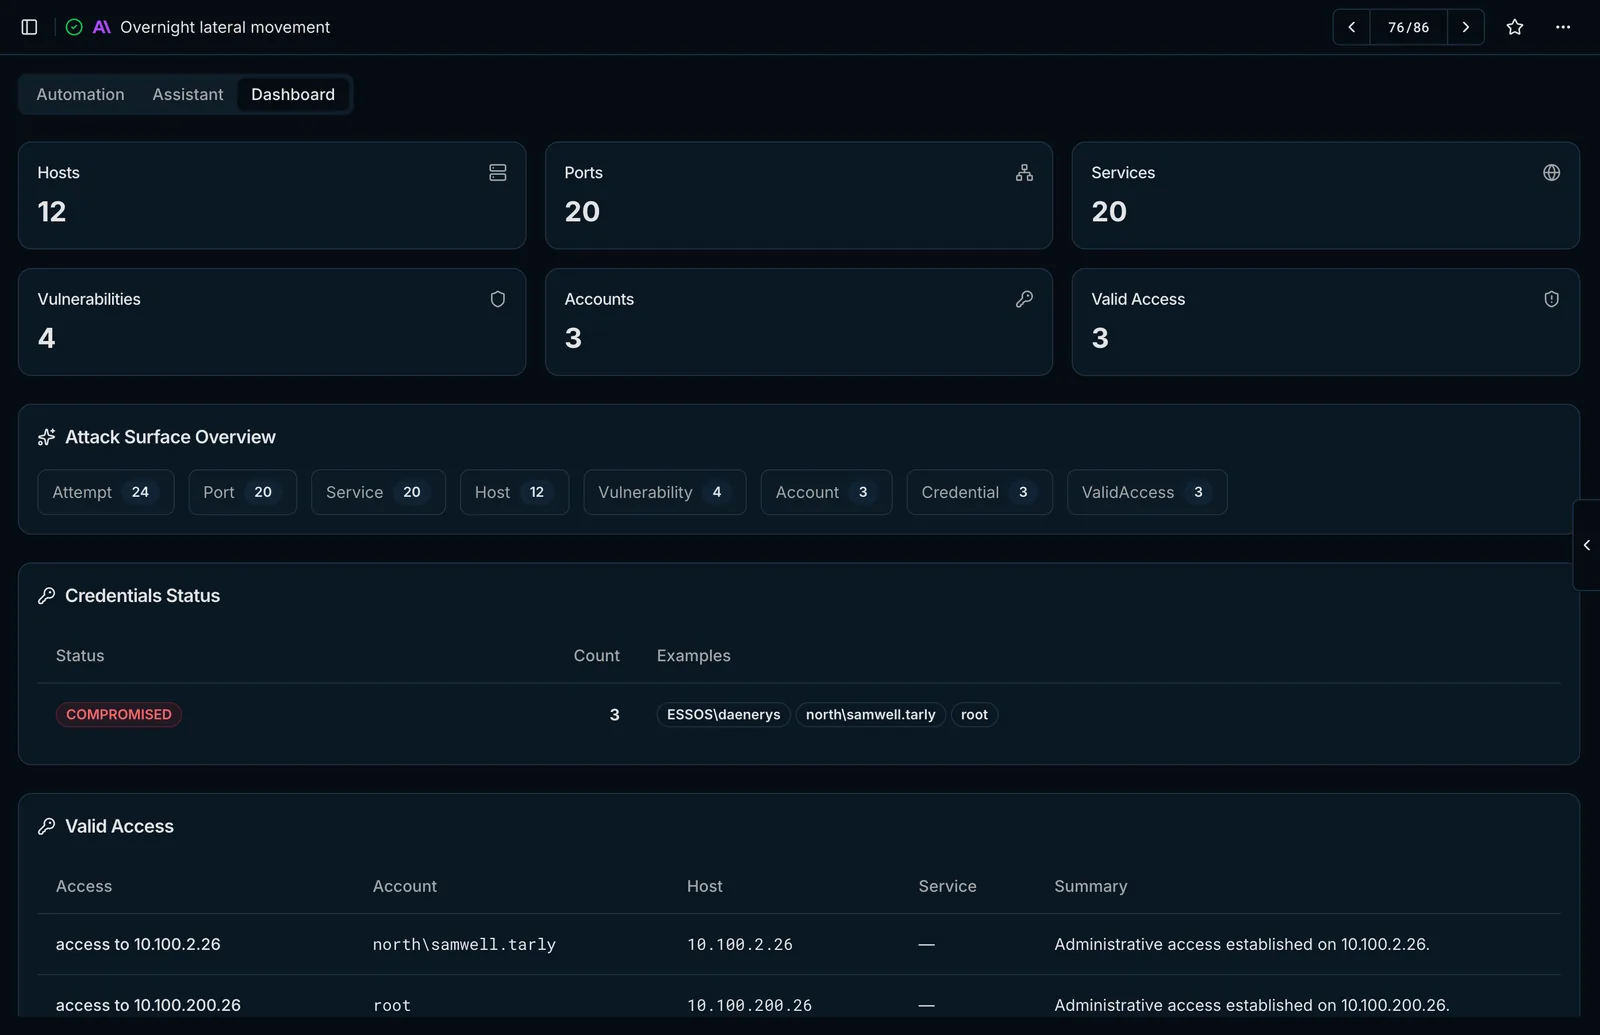
With the knowledge graph enabled, the flow's Dashboard → Analytics tab renders the graph as it grows:
- Main Attack Chain — hosts, ports, services, vulnerabilities, confirmed access and accounts.
- Action Chain, Infrastructure, Access Chain and Priv Esc Chain views.
- A timeline scrubber to replay how the picture developed, plus tables of open ports, detected CVEs and credential status.
Last updated on